
September 2026
CVE-2026-86060: MikroTik RouterOS MikroTrick policy-mask privilege escalation
MikroTik RouterOS policy-mask manipulation can escalate privileges. Upgrade the affected release, restrict untrusted SSH access, and inspect users, scripts and configuration even when the router does not report a Flagged state.
CVE-2026-76461: Cisco Secure Email Gateway crafted-email root command execution
Cisco Secure Email Gateway SQL injection can give unauthenticated attackers root command execution. Preserve mail and network evidence, match the AsyncOS upgrade path, and use Cisco TAC when compromise is suspected.
CVE-2026-58704: Pixel cellular-modem privilege escalation
The exploited Pixel cellular-modem flaw can bypass permission checks. Install the current Pixel update, restart, and verify the security patch level; a successful update does not establish whether earlier exploitation occurred.
CVE-2026-76460: Cisco ISE authentication bypass is actively exploited
Cisco reports active exploitation of an ISE and ISE-PIC authentication bypass that can lead to root access. Check every node, preserve off-device evidence, and separate patch installation from investigation and trusted recovery.
RPKI, IRR, and ROA MaxLength: Routing Hygiene for Enterprises That Own Prefixes
A routing-hygiene guide for enterprises that announce public prefixes, covering RPKI ROAs, IRR objects, ROA maxLength risk, and provider turn-up checks.
Fix Sticky Wi-Fi Clients: 802.11k/v/r, Minimum RSSI, and Roaming Tests
A practical sticky-client Wi-Fi guide: AP placement, transmit power, 802.11k/v/r, minimum RSSI, Apple behavior, controller settings, and roaming tests.
RouterOS Device Mode Can Silently Disable PisoWiFi HotSpot
Inspect RouterOS device mode and HotSpot's inactive reason before rebuilding a PisoWiFi portal. Preserve feature overrides, paid-session records and local recovery before any physically confirmed, rebooting mode change.
DNS Privacy vs DNS Filtering: Stop Mixing Up the Jobs
A DNS guide explaining the difference between encrypted DNS, DNSSEC, Protective DNS, malware filtering, parental controls, and resolver bypass.
Moving Beyond SMS MFA: A Household Migration Plan
A household MFA migration plan for moving from SMS codes to authenticator apps, passkeys, security keys, recovery codes, and carrier protections.
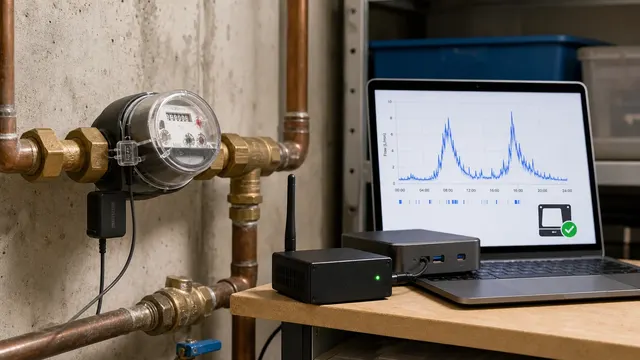
Local Water Meter Monitoring: Privacy, Radio Data, and Safe Setup
Build a receive-only water-monitoring workflow without opening or modifying utility equipment. Check authorization, radio and cloud dependencies, data retention, leak alerts, and what detailed usage can reveal about a household.