
September 2026
Why Your Local Model Server Fails On User Two
Diagnose overlapping model requests through latency, queueing, failures and memory use. Compare consistent prompt workloads and cache conditions before setting admission limits from single-user throughput or another server's benchmark.
Email Is the Root Account: Lock It Down Before Anything Else
Protect the mailbox that receives high-impact account resets and map its actual recovery dependencies. Review hidden access and independent fallback methods without assuming every linked service uses the same recovery model.
How to Audit Your Exposed Services
A practical exposure-audit guide for finding public ports, reverse proxies, tunnels, UPnP, IPv6 paths, vendor clouds, and forgotten services.
Trusted Proxies Are an Authentication Boundary: Stop X-Forwarded-For Spoofing
Define the intended reverse-proxy chain, reject untrusted forwarding headers and block unauthorized direct-origin access. Plan allowed and denied path tests while keeping client IP attribution separate from user authentication.
Rebuild A Dead Proxmox Host: What PBS Does Not Restore
Identify the host networking, storage, credentials and recovery records that guest backups do not establish. Plan an isolated Proxmox rebuild around the scope of your actual backup jobs.
What to Do When a Device Hits CISA KEV
When a KEV-listed vulnerability may affect your device, confirm model, build, feature and exposure. Preserve useful evidence, contain applicable risk and follow supported remediation without assuming the device is already compromised.
Edge Device Patch Priority Playbook
A patch-priority playbook for routers, firewalls, VPN gateways, NAS appliances, and other internet-facing edge devices.
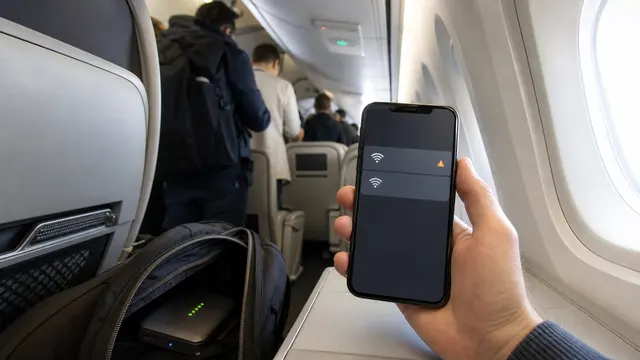
Evil Twin Wi-Fi on Planes and Hotels: How to Verify the Hotspot
A familiar SSID is not proof of a legitimate airline or hotel hotspot. Use this verification workflow, then learn what PMF, HTTPS, captive portals, and VPNs can and cannot protect.
Why MikroTik PCC Breaks HotSpot On Dual WAN
Understand MikroTik HotSpot's default-table limitation before applying PCC exclusions. Diagnose local routing separately from general load balancing, then plan portal, payment and WAN-failure checks against a known-working path.
Media API Keys in Access Logs: Check for Exposure and Rotate Safely
Trace where media API keys may persist in URLs, logs, support bundles and backups. Search without exposing secrets, restrict original evidence, share redacted copies and rotate affected credentials across dependent integrations.