
Network Security
Defensive network security guides for segmentation, VPNs, firewall policy, identity protection, secure remote access, logging, and recovery.
Patching Is Not Eradication: When An Edge Appliance Must Be Rebuilt
Decide whether supported remediation can restore trust in a compromised edge appliance. Coordinate containment, evidence preservation, configuration review and credential changes before rebuilding or reconnecting it.
When The Firewall Is Compromised, What Else Must Be Rotated?
Map firewall sessions, tokens, VPN secrets, certificates and connected identity services after compromise. Rotate affected trust in dependency order while separating confirmed exposure from systems that were merely reachable.
Your Network Configuration Is A Security Log
Use preserved configuration exports and normalized comparisons to detect changes in network access, routing and logging. Correlate differences with identity and runtime evidence; a clean diff does not prove a clean device.
Is Your Self-Hosted AI Actually Private? Audit Every Data Path
A practical audit for local AI prompts, cloud model selection, web and vision sidecars, exposed APIs, logs, and backups before sensitive data enters the system.
Why Port Forwarding Fails: Diagnose Double NAT, CGNAT, and IPv6 Before Buying Gear
A topology-first troubleshooting guide for failed port forwards: public IP checks, double NAT, CGNAT, IPv6 firewall rules, UPnP, VPN, and tunnel alternatives.
The First 60 Minutes Of A Small-Office Cyber Incident
Organize the first hour around clean communications, safety-aware containment, backup protection and an evidence timeline. Prepare a responder handoff without confusing isolation or elapsed time with completed recovery.
RPKI, IRR, and ROA MaxLength: Routing Hygiene for Enterprises That Own Prefixes
A routing-hygiene guide for enterprises that announce public prefixes, covering RPKI ROAs, IRR objects, ROA maxLength risk, and provider turn-up checks.
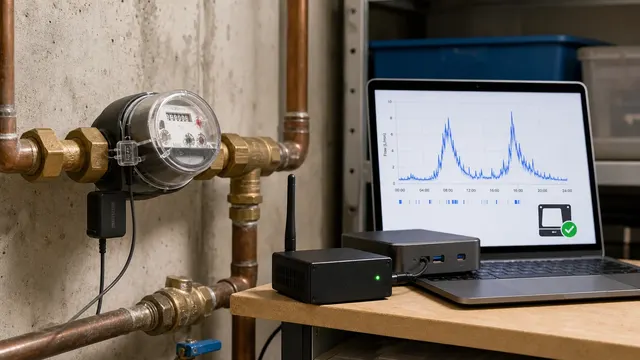
Local Water Meter Monitoring: Privacy, Radio Data, and Safe Setup
Build a receive-only water-monitoring workflow without opening or modifying utility equipment. Check authorization, radio and cloud dependencies, data retention, leak alerts, and what detailed usage can reveal about a household.
How to Audit Your Exposed Services
A practical exposure-audit guide for finding public ports, reverse proxies, tunnels, UPnP, IPv6 paths, vendor clouds, and forgotten services.
Trusted Proxies Are an Authentication Boundary: Stop X-Forwarded-For Spoofing
Define the intended reverse-proxy chain, reject untrusted forwarding headers and block unauthorized direct-origin access. Plan allowed and denied path tests while keeping client IP attribution separate from user authentication.