
Vulnerability Management
Tenable Enclave Security Patch SC-202610.2 Updates PHPNew!!
Tenable released SC-202610.2 for Tenable Enclave Security. Apply the correct patch, verify PHP and service health, test operations, and retain evidence.
Tenable Security Center Patch SC-202610.2 Updates PHPNew!!
Tenable released SC-202610.2 for Tenable Security Center. Apply the correct patch, verify PHP and service health, test operations, and retain evidence.
Tenable Enclave Security Patch SC-202610.1 Updates PHPNew!!
Tenable released SC-202610.1 for Tenable Enclave Security. Apply the patch, verify PHP and service health, test operations, and retain evidence.
Tenable Security Center Patch SC-202610.1 Updates PHPNew!!
Tenable released SC-202610.1 for Tenable Security Center. Apply the patch, verify PHP and service health, test operations, and retain evidence.
Tenable Nessus 10.12.5 Fixes Nine Vulnerabilities
Nessus 10.12.5 fixes nine vulnerabilities requiring authenticated users or privileged attackers. Update the scanner application, preserve configuration and scan history, and coordinate running jobs; current scan plugins alone do not establish fixed scanner software.
What to Do When a Device Hits CISA KEV
When a KEV-listed vulnerability may affect your device, confirm model, build, feature and exposure. Preserve useful evidence, contain applicable risk and follow supported remediation without assuming the device is already compromised.
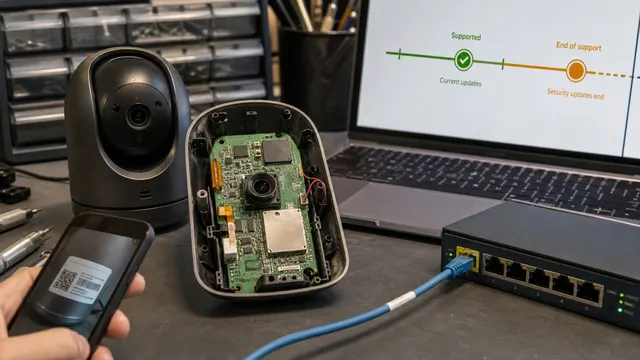
IoT Device Security Checklist: Firmware, Updates, and End of Support
Review an IoT device's firmware source, update and recovery path, vulnerability-disclosure record, exposed services, support dates, and isolation options before purchase and at each lifecycle review.
Is My Router Affected by This CVE? Model, Firmware, and Exposure Checks
Match the exact router model, hardware revision, firmware build, affected feature, and management exposure before acting on a CVE headline. Then route known exploitation or compromise to the appropriate patch, rebuild, rotation, or replacement runbook.
Resilience Planning for Cisco Networks: Patch, Shield, Replace, or Segment
A practical resilience model for Cisco networks should classify each exposure into patch, shield, replace, or segment, with owners, deadlines, and evidence.
Live Protect and Runtime Vulnerability Shielding for Network Infrastructure
Assess Cisco Live Protect only for supported platforms, releases, and vulnerabilities, with monitoring and rollback while permanent fixes are tested; runtime shielding does not replace patching.