
Incident Response
What to Do When a Device Hits CISA KEV
When a KEV-listed vulnerability may affect your device, confirm model, build, feature and exposure. Preserve useful evidence, contain applicable risk and follow supported remediation without assuming the device is already compromised.
Restore From a Compromised Backup Without Reinfecting Production
Recover needed data from suspect backups in isolation, rebuild executable components from trusted sources, replace exposed credentials, and require application checks plus security review before reconnecting.
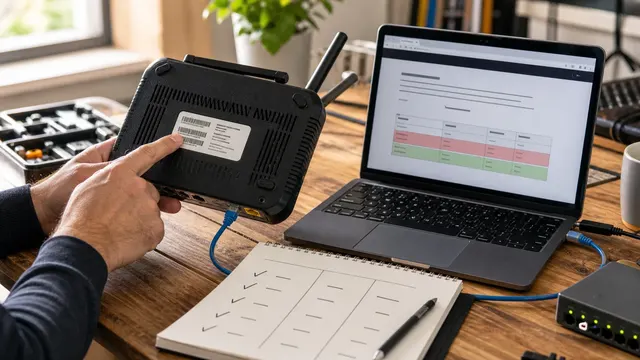
Is My Router Affected by This CVE? Model, Firmware, and Exposure Checks
Match the exact router model, hardware revision, firmware build, affected feature, and management exposure before acting on a CVE headline. Then route known exploitation or compromise to the appropriate patch, rebuild, rotation, or replacement runbook.
WordPress Core Under Active Exploitation: Verify the Fix and Investigate Possible Compromise
Updating WordPress core is only the first step. Use this checklist to verify versions, checksums, users, cron, uploads, logs, WAF data, and rebuild criteria.