
CISA KEV
CVE-2026-76461: Cisco Secure Email Gateway crafted-email root command execution
Cisco Secure Email Gateway SQL injection can give unauthenticated attackers root command execution. Preserve mail and network evidence, match the AsyncOS upgrade path, and use Cisco TAC when compromise is suspected.
CVE-2026-86060: MikroTik RouterOS MikroTrick policy-mask privilege escalation
MikroTik RouterOS policy-mask manipulation can escalate privileges. Upgrade the affected release, restrict untrusted SSH access, and inspect users, scripts and configuration even when the router does not report a Flagged state.
CVE-2026-67277: MikroTik RouterOS btest unauthenticated memory disclosure and denial of service
Missing authentication in RouterOS btest can disclose kernel memory or interrupt service. Check the service and release, then install the supported fix; restricting SSH alone does not establish that this btest flaw is resolved.
What to Do When a Device Hits CISA KEV
When a KEV-listed vulnerability may affect your device, confirm model, build, feature and exposure. Preserve useful evidence, contain applicable risk and follow supported remediation without assuming the device is already compromised.
Edge Device Patch Priority Playbook
A patch-priority playbook for routers, firewalls, VPN gateways, NAS appliances, and other internet-facing edge devices.
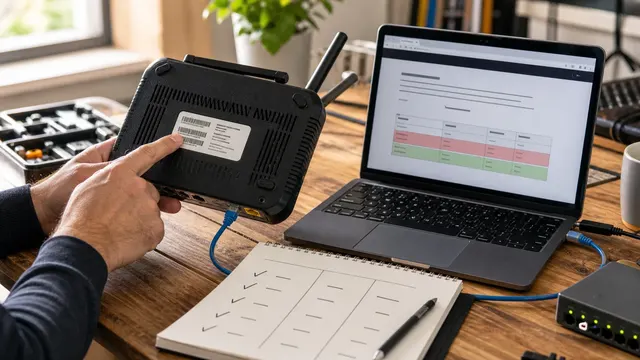
Is My Router Affected by This CVE? Model, Firmware, and Exposure Checks
Match the exact router model, hardware revision, firmware build, affected feature, and management exposure before acting on a CVE headline. Then route known exploitation or compromise to the appropriate patch, rebuild, rotation, or replacement runbook.
WordPress Core Under Active Exploitation: Verify the Fix and Investigate Possible Compromise
Updating WordPress core is only the first step. Use this checklist to verify versions, checksums, users, cron, uploads, logs, WAF data, and rebuild criteria.