
September 2026
2.4 GHz vs 5 GHz vs 6 GHz: What Should Go Where?
A practical Wi-Fi band-planning guide explaining which devices belong on 2.4 GHz, 5 GHz, and 6 GHz networks in Wi-Fi 6E and Wi-Fi 7 homes.
Where Should You Put Your Wi-Fi Access Points?
A practical Wi-Fi AP placement guide for homes and small offices, covering ceiling APs, wired backhaul, multi-floor layouts, RF obstacles, and validation.
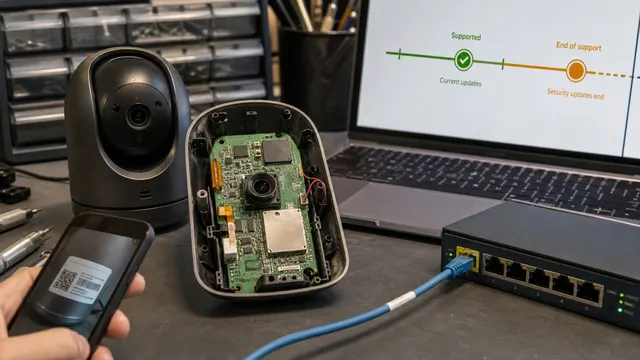
IoT Device Security Checklist: Firmware, Updates, and End of Support
Review an IoT device's firmware source, update and recovery path, vulnerability-disclosure record, exposed services, support dates, and isolation options before purchase and at each lifecycle review.
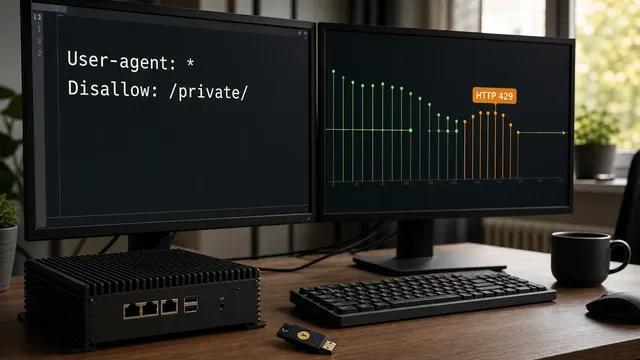
How to Block AI Scrapers: robots.txt, Rate Limits, and Access Control
State crawler preferences with robots.txt, enforce request policies with bot controls and rate limits, and authenticate private content. Test exceptions for legitimate traffic and retain logs without assuming every unwanted scraper is blocked.
Build a Homelab Service Catalog Before You Forget Everything
A practical homelab service catalog guide for tracking what runs where, who uses it, how it is backed up, and how to recover it.
Homelab SSO: Authentik vs Authelia vs Pocket ID
A practical homelab SSO comparison covering Authentik, Authelia, Pocket ID, OIDC, SAML, proxy auth, passkeys, MFA, and recovery planning.
Check Point Confirms Active Exploitation of VPN RCE CVE-2026-85102
Check Point reports active exploitation of a pre-authentication VPN certificate-handling flaw. Match Security Gateway or Spark builds to the supported fix, preserve logs, and investigate suspicious Mobile Access logins separately from patch installation.
Is My Router Affected by This CVE? Model, Firmware, and Exposure Checks
Match the exact router model, hardware revision, firmware build, affected feature, and management exposure before acting on a CVE headline. Then route known exploitation or compromise to the appropriate patch, rebuild, rotation, or replacement runbook.
Linux Failure Injection Lab: Test systemd, Disk, DNS, and Recovery
Run bounded Linux failure-injection tests for systemd crashes, full and read-only filesystems, DNS and network loss, watchdogs, external alerts, rollback, and user-facing recovery without using production as the target.
Palo Alto Networks Revises GlobalProtect Privilege Escalation Fixes
Palo Alto Networks added release ETAs for GlobalProtect CVE-2026-0307 fixes. Map both client and infrastructure updates, validate, and retain evidence.